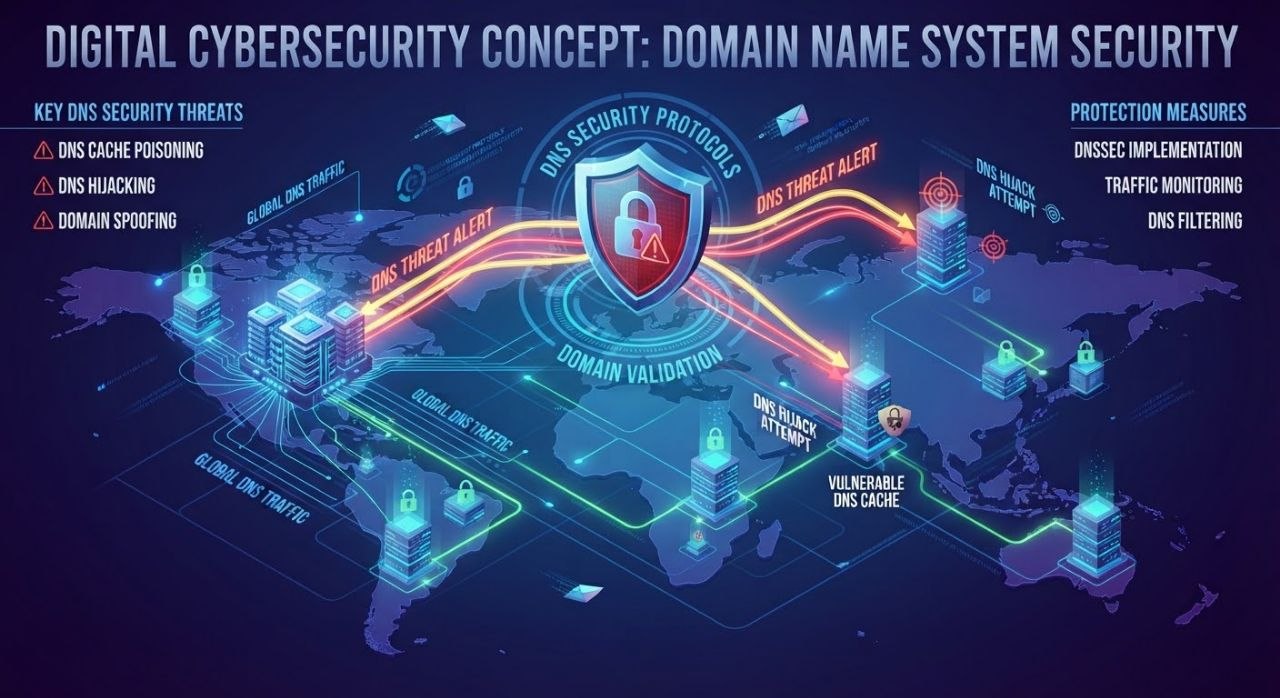
Hackers successfully hijacked several Google domains and obtained unauthorized HTTPS certificates after compromising third-party operators running multiple country-code top-level domain (ccTLD) registries. Disclosed by Google on October 6, 2026, the sophisticated attack targeted the domain namespaces for Ghana (.gh), Sierra Leone (.sl), and American Samoa (.as).
According to technical details published by Google’s Chrome Secure Web and Networking Team and security reports, the attackers did not breach Google’s own internal infrastructure or systems. Instead, the unauthorized actors targeted the third-party operators responsible for managing the targeted ccTLD suffixes. By altering authoritative DNS records, the attackers were able to redirect traffic and secure rogue TLS certificates for multiple high-profile Google properties and other major global brands.
Swift Mitigation and Browser Protection
Upon discovering the security incident, Google moved quickly to contain the threat. The tech giant confirmed that its Chrome web browser immediately blocked the unauthorized HTTPS certificates using CRLSets. Google also collaborated directly with the issuing Certificate Authorities (CAs) to revoke the fraudulent certificates and extend protection to clients across the broader internet ecosystem.
Security researchers noted that compromising ccTLD registries to trick Certificate Authorities into issuing trusted digital certificates is a known, albeit dangerous, attack vector. Although Google emphasized that the issuing CAs did not act improperly given the altered DNS validation pathways, the incident underscores ongoing vulnerabilities in third-party domain infrastructure.
Broader Impact and Ongoing Investigations
After examining Certificate Transparency (CT) log data, Google discovered that the attack extended well beyond its own corporate properties. Additional organizations and leading global brands utilizing widely used online services also appear to have been impacted by the same coordinated campaign.
Google has begun notifying affected organizations where possible and blocked additional certificates discovered during its log reviews. Operators for the affected ccTLD registries—including those for Ghana, Sierra Leone, and American Samoa—have faced intense scrutiny following the security breaches, though complete details regarding how the initial registry access was achieved remain under ongoing investigation.